
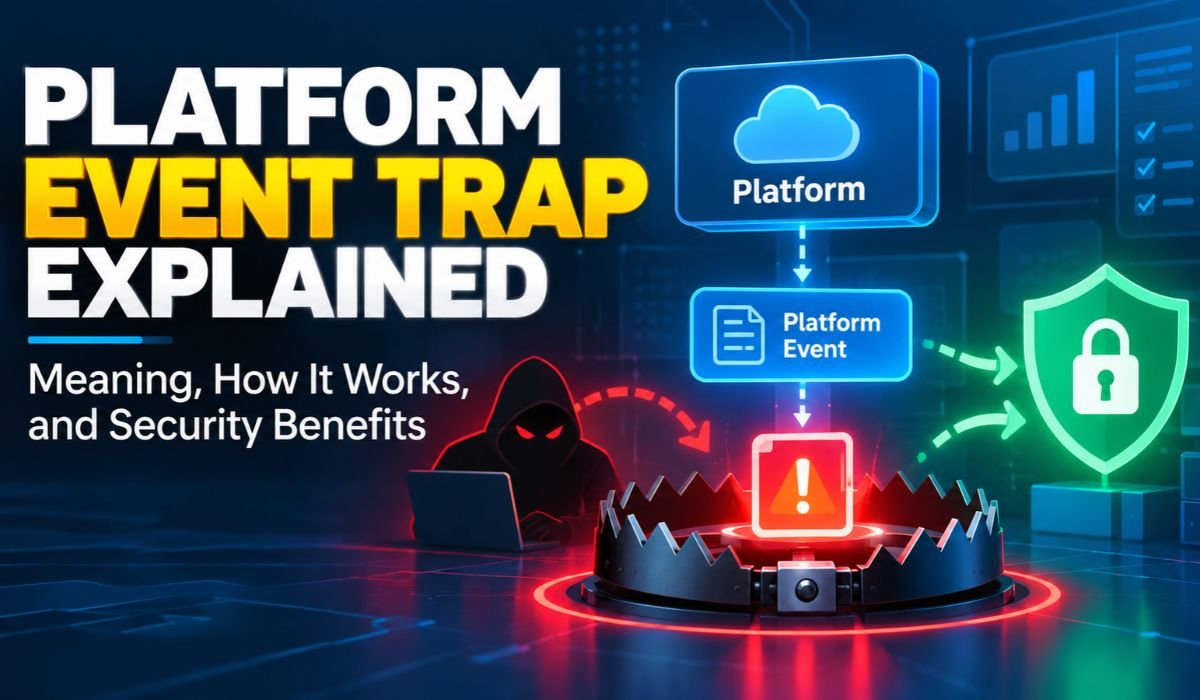
Modern software development moves quickly, but security threats can move just as fast. Every code update, cloud configuration change, and automated deployment creates opportunities for mistakes or unauthorized activity. Organizations need security controls that can respond immediately rather than waiting for someone to discover a problem.
This is where Platform Event Trap becomes important. It describes an event-driven security approach that detects specific activities, checks them against established policies, and triggers protective actions when necessary.
For example, imagine a developer accidentally including a confidential API key in a code update. A properly configured security workflow can detect the exposed credential, block the change, and initiate remediation before the problem spreads.
Understanding Platform Event Trap helps developers, security professionals, and businesses strengthen their software delivery processes. This guide explores its meaning, working principles, benefits, applications, challenges, and best practices in 2026.
What Is a Platform Event Trap?
A Platform Event Trap is an event-driven security enforcement pattern that responds to activities violating predefined security policies. It can monitor events within software repositories, CI/CD pipelines, cloud infrastructure, and automated workflows.
Unlike traditional security monitoring, which often focuses on generating alerts, this approach connects event detection with enforcement actions.
A Platform Event Trap might stop an unauthorized deployment, prevent an unsafe code merge, or initiate the revocation of compromised credentials.
Importantly, Platform Event Trap is not a universally standardized cybersecurity product or formal technical category. The term describes a security approach that organizations can implement using existing automation platforms, event listeners, policy engines, and security integrations.
Its central purpose is simple: identify risky activity early and respond before it creates a larger security problem.
Quick Bio Information About Platform Event Trap
| Information | Details |
|---|---|
| Name | Platform Event Trap |
| Category | Cybersecurity |
| Main Concept | Event-Driven Security Enforcement |
| Primary Purpose | Detecting And Responding To Policy Violations |
| Security Approach | Automated Policy-Based Response |
| Common Environment | CI/CD Pipelines |
| Additional Environment | Cloud Infrastructure |
| Event Sources | Repositories, Identity Systems, And Build Platforms |
| Core Technology | Event Listeners And Automation |
| Policy Evaluation | Security Rules And Authorization Checks |
| Common Response | Blocking Unsafe Operations |
| Credential Protection | Secret Detection And Revocation Workflows |
| Cloud Security Role | Configuration And Access Enforcement |
| DevOps Application | Secure Software Delivery |
| Identity Security | Service Accounts And Machine Credentials |
| Main Advantage | Faster Risk Containment |
| Main Challenge | False Positives And Workflow Disruption |
| Governance Support | Audit Logs And Policy Records |
| Relevant Frameworks | NIST CSF, NIST SSDF, And OWASP Guidance |
| Technology Outlook | Policy-As-Code And Automated Security Controls |
How Does a Platform Event Trap Work?
A Platform Event Trap operates through a connected process involving event detection, policy evaluation, and automated enforcement.
The process begins when an activity occurs within a monitored platform. This might involve a developer submitting code, an application requesting privileged access, or an administrator changing cloud settings.
An event listener or platform integration captures the relevant information and passes it to a security control. A policy engine then evaluates the event against predefined rules.
If the activity meets security requirements, the workflow continues normally. If it violates a policy, the enforcement system can block the operation, pause the workflow, or initiate another approved response.
The system should also record the event and its outcome. These records help security teams investigate incidents, review enforcement decisions, and improve policies.
Reliable implementation depends on accurate event data, appropriate permissions, and carefully tested response mechanisms.
Key Components of a Platform Event Trap
Several technical components work together to support effective event-driven security.
The event source generates information about activities occurring within a system. Common sources include Git repositories, cloud platforms, identity providers, and automated deployment tools.
Event listeners capture relevant activity through mechanisms such as webhooks, platform events, or security integrations.
A policy engine evaluates the captured information against organizational rules. These rules may cover access permissions, deployment approvals, software signatures, or credential handling.
The enforcement mechanism performs the selected response. Depending on its permissions, it may stop a build, reject a deployment, or request credential rotation.
Audit logging completes the process by recording what happened and why. Together, these components create a security workflow that can react quickly while remaining accountable.
Why Platform Event Traps Matter in Cybersecurity
Security incidents often become more damaging when organizations cannot respond quickly.
An exposed credential may provide unauthorized access. An insecure software release may introduce vulnerabilities into production. An unapproved infrastructure change may weaken existing protections.
Platform Event Traps help reduce these risks by connecting detection with immediate policy enforcement.
They are particularly useful in environments where software changes occur frequently and manual reviews cannot examine every event in real time.
However, automation does not guarantee complete protection. Its effectiveness depends on the quality of security rules, the events being monitored, and the reliability of enforcement integrations.
When implemented carefully, event-driven controls strengthen existing security operations rather than replacing human judgment.
Common Security Events That Trigger Platform Event Traps
Different security events require different responses.
One common example involves exposed API keys or passwords discovered during repository scanning. A security workflow may prevent the affected change from merging while initiating credential remediation.
Unauthorized code changes provide another example. If a pull request bypasses required approvals, repository protection rules can reject the merge.
Deployment events are equally important. A release containing an unsigned artifact may be blocked until its integrity is verified.
Cloud configuration changes can also trigger enforcement. For instance, a policy engine might detect a storage resource configured for unintended public access.
Suspicious service account activity may require investigation or additional authorization.
The key is selecting events that represent meaningful risks and connecting them to proportionate security responses.
Platform Event Trap in CI/CD Pipelines
Continuous Integration and Continuous Delivery, commonly called CI/CD, automate software building, testing, and deployment.
These processes improve development speed but also create opportunities for security problems to spread automatically.
Platform Event Trap controls can strengthen CI/CD security by checking important events throughout the software delivery lifecycle.
During code submission, repository policies may require successful security scans and authorized reviews. During builds, automated checks can identify exposed secrets, vulnerable dependencies, or missing artifact signatures.
Before deployment, release policies can verify approvals and required security conditions.
For example, a pipeline may refuse to promote an application when its software artifact fails signature verification.
This approach supports DevSecOps by integrating security enforcement into development workflows instead of relying entirely on checks performed after deployment.
Platform Event Trap and Cloud Security
Cloud infrastructure changes constantly as organizations create resources, update applications, and adjust permissions.
Event-driven security controls can help identify risky changes and respond according to established policies.
Consider a cloud storage configuration that unexpectedly allows public access. A monitoring integration may detect the change and initiate a corrective workflow.
Similarly, an unauthorized change to a privileged identity policy may trigger an investigation or restriction.
Cloud configuration drift is another important concern. Drift occurs when infrastructure settings move away from an approved baseline.
Some automation systems can restore trusted configurations, although rollback must be carefully designed to avoid disrupting legitimate services.
Platform Event Traps are therefore useful for cloud governance, especially when combined with identity management, infrastructure-as-code, and continuous configuration assessment.
Platform Event Trap and Non-Human Identity Security
Modern applications depend heavily on Non-Human Identities, including service accounts, automation tokens, machine credentials, and application identities.
These identities allow systems to communicate and perform tasks without direct human involvement.
Unfortunately, compromised machine credentials can provide attackers with powerful access to sensitive environments.
Platform Event Trap controls can help enforce rules governing these identities.
For example, an automated workflow might detect a service account requesting permissions outside its approved scope. The system could pause the activity and require further authorization.
Secret scanning can also identify accidentally exposed credentials and initiate rotation or revocation procedures.
Effective protection requires least-privilege access, reliable identity inventories, credential lifecycle management, and clear ownership of automated accounts.
Security Benefits of Platform Event Traps
The greatest advantage of Platform Event Traps is their ability to shorten the time between identifying a security violation and taking action.
Instead of waiting for manual intervention, organizations can automatically block selected high-risk operations.
This improves deployment security by preventing unauthorized or noncompliant changes from progressing through software delivery pipelines.
Credential protection can also improve when secret detection connects directly to remediation workflows.
Another benefit is consistency. Automated policies apply defined requirements across repeated operations, reducing dependence on individual decisions.
Event records also support internal reviews, incident investigations, and compliance activities.
However, these benefits are strongest when enforcement rules are accurate, properly maintained, and aligned with business needs.
Real-World Applications of Platform Event Traps
Practical examples make the concept easier to understand.
Imagine a software team preparing a production release. During verification, the pipeline discovers that the application artifact lacks a valid signature. An enforcement rule blocks deployment until the issue is corrected.
In another scenario, a developer accidentally commits a confidential token. Repository scanning detects the secret, preventing the affected change from merging. A connected credential management system can then initiate revocation.
A cloud security workflow might identify an unauthorized firewall change and request corrective action.
An identity platform could also detect a privileged service account operating outside an approved deployment window.
These are illustrative scenarios rather than claims about particular organizations. They demonstrate how event-driven enforcement can prevent security violations from progressing unnoticed.
Platform Event Trap vs. Traditional Security Monitoring
Traditional security monitoring and Platform Event Traps serve related but different purposes.
Monitoring systems collect information about system activity, detect suspicious behavior, and generate alerts for investigation.
Platform Event Trap implementations go further by connecting selected events to automated enforcement actions.
For example, monitoring might notify a security team that a deployment lacks approval. An enforcement control could prevent that deployment from proceeding.
Traditional monitoring remains essential because not every suspicious event should trigger an automatic restriction.
Some incidents require investigation, additional context, or human judgment before action.
The strongest security strategies combine visibility, reliable alerts, automated controls, and documented response procedures.
How to Implement a Platform Event Trap
Implementing a Platform Event Trap begins with identifying activities that present significant security risks.
Organizations should first examine critical workflows involving deployments, privileged access, credentials, and infrastructure changes.
Next, security teams define clear policies describing which events are permitted and which require intervention.
Suitable integrations must then connect event sources with policy evaluation and enforcement systems.
For example, a repository security rule might require secret scanning to pass before code can merge.
Before activating blocking controls, teams should test expected behavior and examine possible false positives.
A controlled rollout is often safer than immediately enforcing every rule across production environments.
Finally, organizations should regularly review audit records, policy effectiveness, and exceptions to keep enforcement accurate and manageable.
Challenges and Limitations of Platform Event Traps
Although automated enforcement offers important advantages, it can also introduce operational challenges.
False positives are a major concern. A poorly configured rule may block legitimate code changes or interrupt necessary deployments.
Integration complexity can create additional difficulties, especially when organizations use multiple development, identity, and cloud platforms.
Automated responses may also produce unintended consequences. Revoking a shared credential or rolling back infrastructure without proper safeguards can disrupt essential services.
Security teams must therefore establish clear ownership, reliable testing procedures, and controlled exception mechanisms.
Another limitation involves incomplete visibility. An event-driven control cannot respond to activities it does not detect.
Successful implementation requires continuous policy maintenance, trustworthy event sources, and appropriate human oversight.
Best Practices and Cybersecurity Standards
Effective Platform Event Trap security begins with carefully selected policies and clearly defined responsibilities.
Organizations should prioritize high-risk activities, apply least-privilege permissions, and test enforcement logic before enabling production restrictions.
Every automated response should generate useful audit information. Security teams should also establish recovery procedures for incorrect blocking decisions.
Established cybersecurity frameworks provide helpful guidance.
The NIST Cybersecurity Framework 2.0 supports structured approaches to governance, detection, response, and recovery.
The NIST Secure Software Development Framework encourages security practices throughout software development.
OWASP resources help teams understand application security, software supply chain risks, and identity-related threats.
These frameworks support the underlying security principles, although they do not formally define Platform Event Trap as a standardized control.
Future of Platform Event Traps in Cybersecurity
As software development becomes increasingly automated, event-driven security enforcement is likely to remain an important area of security engineering.
Policy-as-code allows organizations to express security requirements in formats that automated systems can evaluate consistently.
Cloud-native platforms also provide more opportunities to connect infrastructure events with security responses.
AI-assisted analysis may eventually help teams prioritize suspicious events and identify patterns requiring investigation.
However, automated decisions still need clear rules, reliable evidence, and human oversight.
The future of Platform Event Trap security is not simply about responding faster. It is about making automated responses more accurate, explainable, and proportionate to actual risks.
Final Thoughts
Platform Event Trap represents a practical approach to strengthening security through event-driven enforcement.
By detecting policy violations and initiating timely responses, organizations can reduce the risk of unsafe deployments, exposed credentials, unauthorized access, and insecure cloud configurations.
Its value is especially clear in CI/CD pipelines, DevSecOps environments, and automated identity management.
Still, successful implementation requires more than automation. Clear policies, careful testing, reliable integrations, and human oversight remain essential.
For organizations building secure digital systems in 2026, the most effective approach combines continuous monitoring with well-governed automated enforcement.
FAQs About Platform Event Trap
What Is a Platform Event Trap in Cybersecurity?
A Platform Event Trap is an event-driven security enforcement approach that detects activities violating predefined policies and triggers appropriate responses. It can help protect software development pipelines, cloud environments, and automated workflows.
How Does a Platform Event Trap Work?
It captures relevant platform events, evaluates them against security policies, and initiates actions when violations occur. Depending on its configuration, the response may involve blocking a deployment, pausing a workflow, or initiating credential remediation.
Is Platform Event Trap a Security Tool?
Not necessarily. Platform Event Trap describes an implementation pattern rather than a universally recognized standalone product. Organizations can build similar controls using repository protection features, policy engines, security scanners, and automation integrations.
Can Platform Event Traps Prevent Cyberattacks?
They can prevent certain unsafe operations and reduce exposure to security risks. However, they cannot guarantee protection against every cyberattack. Their effectiveness depends on accurate policies, reliable detection, and appropriate enforcement capabilities.
How Are Platform Event Traps Used in CI/CD Pipelines?
They can enforce security requirements during code merging, building, testing, and deployment. Common applications include blocking releases with failed security checks, missing approvals, exposed secrets, or unverified artifacts.
What Is the Difference Between a Platform Event Trap and a Security Alert?
A security alert informs users or systems about an event requiring attention. A Platform Event Trap connects qualifying events to enforcement actions, potentially stopping unsafe operations automatically.
Can Platform Event Traps Improve Cloud Security?
Yes. Event-driven controls can detect cloud configuration violations, unauthorized changes, and suspicious identity activity. When integrated with suitable systems, they can initiate restrictions, corrective workflows, or security investigations.
What Are the Main Limitations of Platform Event Traps?
Their limitations include false positives, integration complexity, incomplete event visibility, and potentially disruptive automated responses. Organizations should address these challenges through testing, policy reviews, controlled permissions, and documented recovery procedures.
Learn more and explore exciting content on: Plangud Explained: Meaning, Uses, Benefits, and Complete Guide


Leave a Reply